

Hyundai and Kia to Invest $816M in First Battery-Dedicated R&D Campus
Prime Highlight Hyundai Motor and Kia will invest ₩1.2 trillion ($816 million) to build their first battery-dedicated R&D facility, the Future Mobility Battery Anseong Campus. The campus aims to strengthen Korea’s competitiveness in the global electrification market and serve as a central hub for battery innovation. Key Facts Covering 111,000 square meters, the campus will handle the full battery development process, from material research to vehicle-level integration. The facility, scheduled for completion in 2026, will feature an AI-based testbed to analyze battery data and enhance product quality. Background Hyundai Motor Co. and Kia announced on Friday that they will invest ₩1.2 trillion ($816 million) to build their first battery-dedicated research and development facilities, marking a major step toward expanding their in-house battery capabilities. The facility, called the Future Mobility Battery Anseong Campus, is under construction in Anseong, Gyeonggi Province, and is scheduled for completion in 2026. The companies held a ceremony to mark the safe progress of the project, attended by senior Hyundai-Kia executives and government officials, including Yang Heui-won, head of Hyundai-Kia R&D, and Gyeonggi Governor Kim Dong-yeon. Yang said the campus will serve as a central hub for Korea’s battery sector, helping connect industries and accelerate technological growth. He added that the facility will strengthen Korea’s competitiveness in the global electrification market. Covering 111,000 square meters, the campus will handle the full battery development process. Hyundai and Kia plan to integrate facilities that support everything from material research and cell production to module packaging and vehicle-level integration. The companies said the site will also feature an AI-based testbed, designed to analyze battery data and improve product quality. Until now, Hyundai and Kia have focused only on early-stage battery work, such as basic cell design and material research. Their new campus will allow them to develop high-performance lithium-ion battery cells for electric and extended-range electric vehicles, with long-term plans to expand into robotics and advanced air mobility. Industry analysts say the move shows growing confidence in the automakers’ internal battery capability. Park Cheol-wan, an automotive engineering professor at Seojeong University, said the campus reflects their readiness to compete with major cell makers. He noted that the project also signals stronger competition in Korea’s battery sector. Construction began in January after months of industry speculation. Experts believe the initiative will help Hyundai and Kia gain more bargaining power and open new opportunities beyond electric vehicles. Read Also : OpenAI Plans Historic IPO with Potential $1 Trillion Valuation by 2026–27

ADEETYA MOHTA (NAGPUR): A 10th-Fail Ideal Son Chose MAA between Parents and Relatives For Protection Of Women and Women Empowerment, Fighting Legal Battle Alone Without an Advocate for His Victim Senior-Citizen Mother in India’s Biggest ₹50-Crore Domestic Violence Case Rs 50 lakhs interim, Arrest warrant through commissioner of police not executed since 16 months
ADEETYA MOHTA (NAGPUR): A 10th-Fail Ideal Son born out of wedlock of Satish Mohta and Kusum Mohta married on 27/11/1977, Son Chose MAA between Parents and Relatives For Protection Of Women, Legal rights, Identity and Women Empowerment, Son Says First Step of women Empowerment Starts Within Our Home Sweet Home, Fighting a Legal Battle all Alone Without an Advocate for His Victim Senior-Citizen Mother in India’s Biggest ₹50-Crore Domestic Violence Case filed on 1/12/2022 Kusum Mohta versus (1) Satish ghevarchand mohta (2) Shravan Satish Mohta (3) Gunisha Shravan Mohta (4) Kamal Ramesh Mohta (5) Ramesh Gheverachand Mohta (6) Sushila Omprakesh Mohta (7) Swayam Omprakash Mohta (8) Sushma rajesh Porwal(munnibai), Rs 50 lakhs interim, 36 Months No recovery No Arrest warrant through commissioner of police Nagpur executed, Victim Defaulter Husband clubbing partying enjoying life and Roaming Scotfree without any action on him, No Action has been taken, senior citizen Victim Fundamental rights has been Violated Article 14, 19 and 21, Justice Delayed is Justice Denied. Adeetya mohta Born with a golden spoon millionaire 10th fail ideal son fighting a legal battle alone without an advocate for his senior citizen mother in India biggest ₹50 crore domestic violence case filed second time as from first old Domestic Violence case additional arrears of ₹36 lakhs uncleared which has also been humbly requested in proceedings for most aggrieved deserving senior citizen victim, encashment of interim maintenance upto ₹7.5 lakhs per month has also been proceeded in session appeal in interest of justice, the recovery relief requested from 8 respondents will be in crores for her stridhan, such as 30% partnership in Hotel shravan’s Adit Bar & Restaurant situated at Rani Jhasi Square Sitabuldi Nagpur, 1203 A wing Flat Surya Apartments Bhula Bhai Desai road Breach Candy Mumbai with other gold, silver and diamonds worth crores with other domestic violence legal rights which is pending as proceedings initiated on merits. A most talked about high profile significant case from Nagpur Swetamber Jain Marwadi highly influential family has drawn Indian citizen’s attention as 10th fail ideal eldest son of victim known as Adeetya Mohta becomes the legal representative, protector and emotional financial pillar against all odds for his senior citizen 65 yrs old mother in a ₹50 crore domestic violence case, even though he received several life threatening. Victim having gotten married at the age of 16 on 27 November 1977 at victim home town in Ujjain M P and deserted victim in Additya house 742 Nelson square Chhindwara Road Nagpur at age of 60, victim somehow opened up and raised her voice of several years of pain, misery, and domestic violence incidents in interest of justice for the first time in 2018 for her legal right and filed first Domestic Violence case. Her first Domestic Violence case complaint was withdrawn due to promises, commitments by husband and also under pressure, threat and fear without receiving all the outstanding interim arrears of ₹36 lakhs which is still pending, the victim for the second time again in December 2022 refilled Domestic Violence case, as commitments were not fulfilled and again face violence, somehow with courage again stood up for her legal rights with the help of her said son Adeetya Mohta as fresh cause of action again arose in October 2022 and for the same online police complaint was initiated and second Domestic Violence case was filed along with earlier domestic violence incidents, that the old and new both (DIR) Domestic Violence report supports the Victim on merits, it’s been almost 7 years of subject matter before Hon’ble trial court, Hon’ble session court and Recently filed 4000 pages approx. petition bunch with 61 caselaws before the Hon’ble high court under writ petition 226 and 227. Adeetya Mohta is personally managing, filing, pleading, hearing, arguments, drafting, the whole legal procedure on his own, attending hearings, submitting applications, making arguments, and ensuring that all of his mother legal rights may kindly be given to her so victim can enjoy her fundamental rights freely as early as possible, that the proud most desired son through a legally registered power of attorney P O A conducting all legal matters. He rose up boldly by breaking the ice ceiling and stereotypes which is unusual and remarkable and motivating influencing to all other men and citizens of India to help victims and we all millions of Indians are proud of him who 24/7 with pride, hardwork and dignity stood all alone to support victim without any member’s help from the family. There are almost 16 cases approx. related to the victim subject matter and others almost about approx 50 cases which has been handled all by Adeetya Mohta, infact ₹50 lakhs approx till November 2025 is pending as the husband has defaulted in paying, arrest warrants issued in 2024 which was not executed its been almost 16 months but No Action, victim is facing medical emergency but still not considered and matter was prolonged delay tactics and mischiefs and son facing several day to day life difficulties and white collar crime but still stood as a rock of Gibraltar and still going strong like an 8th wonder of the world from the orange city Nagpur. Adeetya Mohta is very optimistic and blindly believes in our Indian constitution and has blind faith in our judiciary and applauds the Government of India for formulating policies to safeguard elderly senior citizens passed in 1999 and others, such as giving first priority to cases of senior citizens in courts. The meaningful strong submissions of Adeetya Mohta is the embodiment of the government measures even though he has never formally obtained a legal degree as he is 10th fail and has studied only up to the 10th standard but has worked hard 24/7 to master the skills and to become relevant meaningful in the proceedings as he is representator of his senior citizen mother in one of the most highest value cases in the country of the domestic violence case of senior citizen lady. His devotion, dedication
7 Steps to Improve Your Online Store with eCommerce SEO Services
Managing an online shop is always a rush: You’re creating something from scratch, crafting a brand and chatting with customers around the world. But let’s face it, the online world is full. Every click matters, and if your store isn’t appearing on Google search results, you’re losing actual sales. In this article, you will learn how to give your store that boost in seven easy and practical steps. 1. Build a Smart Keyword Plan Use tools like Google Keyword Planner or Ahrefs to discover search phrases with high volume. Instead of aiming for broad terms like “shoes” or “jackets”, hit them with more extreme ones like “women’s waterproof hiking boots” and “men’s leather travel jackets”. After you’ve done that, sprinkle those keywords naturally into your page titles, product descriptions and image tags. 2. Optimise Every Product Page Be sure to include thorough, honest descriptions that are written in a way that shows off your product’s best features. Strive to keep it conversational, not stuffy, and use bullet points to help split details up when they appear. You can’t forget your meta titles and descriptions: the tiny bit of text that shows up on Google search results. Write them naturally and invitingly, using your keywords. 3. Make Your Site Fast and Mobile-Friendly A slow page can cause visitors to leave before they even see the goods you sell. Use a free tool like Google PageSpeed Insights to see what’s slowing down your site. Speed problems are fixable by compressing big images, deactivating bloated plugins and using a good hosting provider. Fifty-seven per cent of shoppers browse and buy on their phones, so yours needs to look good on small screens. 4. Keep Your Website Organised Your navigation menu should make sense; group similar items together, and use simple categories and subcategories. For instance, if you sell jewellery, separate your products into “Earrings”, “Bracelets”, and “Necklaces”. Link to related products or blog posts to help shoppers explore more of your site. “Necklaces” – search engines love this, too, because it helps them understand how your pages connect. 5. Share Content That Builds Trust Create useful content that answers questions or addresses pain points your customers experience. For instance, if you sell furniture, create content around “Styling a Small Living Room” or “Choosing the Best Dining Table for Your Home”. Good content keeps your customers coming back. It can also garner backlinks from other sites, which is good for your authority and rankings. 6. Use Customer Reviews to Your Advantage When customers see other people happy with their purchase, they’re more likely to trust your store. After buying, ask your happy customers to share their thoughts, say in a follow-up email or with small thank-you discounts. And they don’t just assist in persuading new customers; they can also make your Google listings pop. Those gold star ratings significantly increase click-through rates. 7. Track Your Progress and Keep Improving SEO isn’t something you set up once; it’s ongoing work that grows stronger the more you refine it. Use tools like Google Analytics to track what’s happening on your site: how much traffic you’re getting and how many visitors turn into buyers. If a page ranks high but doesn’t convert, look if there’s something missing in your product images that needs an upgrade, or your call-to-action could be clearer. Grow Your Store with Smart SEO Getting your store out there doesn’t just happen overnight, but the work you put in always pays off. If you follow these steps alongside an ecommerce SEO services, then you’re planning for future growth in your business. Remember to keep learning, keep testing and refining. Before long, you’ll be getting more qualified traffic and a stronger brand that cuts through the noise of the crowded online space. Disclaimer – This article is a work of original content created for public relations and informational purposes only. It may be published across multiple digital platforms with the full knowledge and consent of the author/publisher. All images, logos, and referenced names are the property of their respective owners and used here solely for illustrative or informational purposes. Unauthorized reproduction, distribution, or modification of this article without prior written permission from the original publisher is strictly prohibited. Any resemblance to other content is purely coincidental or used under fair use policy with proper attribution. Read Also : 6 Essential Tips for Safely Using a Pallet Jack
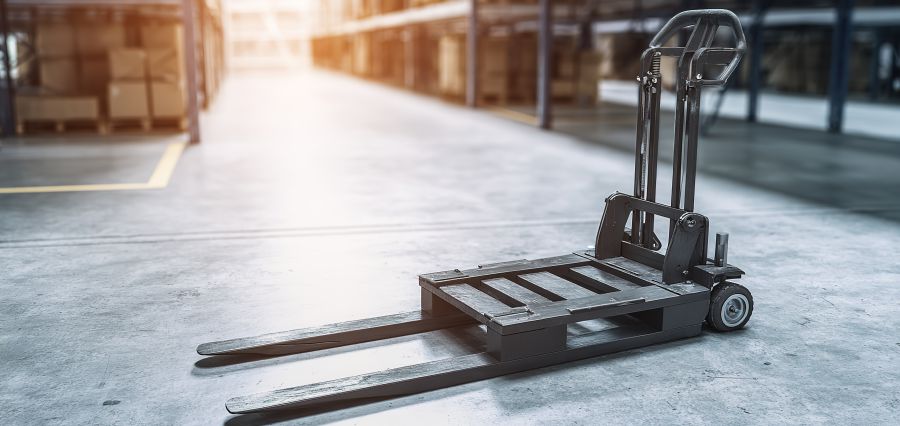
6 Essential Tips for Safely Using a Pallet Jack
Whether you have a warehouse, retail store or logistics facility, pallet jacks are essential equipment for transporting heavy things around. They seem like a simple thing, but misuse can lead to injury or ruin goods. Here are six crucial tips to assist you in using pallet jacks safely and properly daily. Inspect the Pallet Jack Before Each Use It only takes a fast look before you drive a pallet jack in to avoid big problems down the line. Inspect for any damage or leaks on the wheels, forks, handle, and hydraulic pump. Ensure the forks move freely and the handle grip is undamaged. Failure to follow this procedure can cause sudden equipment failure under load. Take a moment to inspect your hand pallet jacks. Trucks do these tasks and avoid downtime and potential hazards on the job. Use the Correct Lifting Technique Bad lifting is a pain in your back, and it makes pallet jack control more difficult. Squat when lifting or setting down a load—knees, don’t waist. Keep both feet on the floor and avoid pulling or jerking with the material you are working with. If the load feels too heavy or awkward, don’t try to handle it yourself. With the right technique, you are always in control and will not suffer work-related injuries caused by overexertion. Secure and Balance the Load Unevenly stacked or loosely piled pallets are often the cause of such accidents. Before you start, lift and check that the weight on your load is evenly distributed between the forks and doesn’t extend too far past the edges of the pallet. To test that everything is secure and nothing shifts significantly when you start driving, gently push the load at the bottom. If you can, strap the items down or shrink wrap them to keep them secure. When the load is evenly distributed, it provides stable and easy traction for the pallet jack. Watch Out for Obstacles and Slopes Tiny hazards such as cords, slight floor inclines, and ramps can be easily overlooked—until they’re not. Look where you are going before the load starts to move to avoid any sudden lurch or overturning. The other occasion not to utilise pallet jacks is when going up and down steep gradients, as it’s difficult to manage the speed of both motions. When in the moderate downhill positions of operation, ensure that the load is always downhill of you and maintain a good grip on the handle. Operate at a Safe Speed Even though pallet jacks move slowly, maintaining speed is crucial. Rushing up the risk of personal injury, product damage, or impacting passersby. Run at a moderate, brisk pace and look out for other workers, especially in cramped aisles. When you change direction or turn a corner, slow down and allow yourself some room. Keeping aware will benefit not only your own safety but also make it easier for others you’re working in tandem with. Park and Store Properly After Use When you are finished with the pallet jack, bury the forks completely and store it in a safe, secure location. Otherwise, the forks sticking up or obstructing aisles could pose a tripping hazard. Proper storage of equipment can also go a long way in keeping it from wearing out too quickly, and storing it properly contributes to neatness at the workstation. A small amount of prevention at the end of a shift goes a long way towards keeping everyone safe and running efficient operations. Safety Starts with Smart Handling Operating a pallet jack is relatively simple, but some smart habits can improve your efficiency. By following the six vital tips listed here, you will improve your overall process and safety at work for everyone involved. Disclaimer – This article is a work of original content created for public relations and informational purposes only. It may be published across multiple digital platforms with the full knowledge and consent of the author/publisher. All images, logos, and referenced names are the property of their respective owners and used here solely for illustrative or informational purposes. Unauthorized reproduction, distribution, or modification of this article without prior written permission from the original publisher is strictly prohibited. Any resemblance to other content is purely coincidental or used under fair use policy with proper attribution. Read Also : Pioneering Approaches: Unlocking Digital Business Growth Strategies
Why is Cyber Insurance a Core Part of Business Continuity?
With the promulgation of the Digital Personal Data Protection Rules, 2025, India finally enters a new era of legally enforceable data protection obligations. For organizations, this is no longer an abstract compliance exercise but a matter of real regulatory, financial, and reputational exposure. What once might have been a single bad day involving a DPDPA incident can now trigger an avalanche of costs addressing forensics, legal defense, breach notifications, crisis communications, vendor fallout, regulatory investigations, and possible civil claims. It is in this paradigm that cyber insurance becomes yet more vital, as a prudent financial backstop in the absorption and management of such risks. However, there is an important nuance present: fines under the DPDPA are still grey in terms of coverage. Though most cyber policies would cover regulatory penalties “where insurable by law,” the Act itself does not mention insurance. Careful risk governance, policy structuring, and wording of coverage thus become absolutely indispensable for any enterprise, said Evaa Saiwal, Practice Head – Liability, Cyber & Speciality Risk at Policybazaar For Business. Consequently, under the DPDPA, cyber insurance is not just a tool for risk management but core to an organization’s ability to absorb the operational and financial shock of a data protection incident. Disclaimer – This article is a work of original content created for public relations and informational purposes only. It may be published across multiple digital platforms with the full knowledge and consent of the author/publisher. All images, logos, and referenced names are the property of their respective owners and used here solely for illustrative or informational purposes. Unauthorized reproduction, distribution, or modification of this article without prior written permission from the original publisher is strictly prohibited. Any resemblance to other content is purely coincidental or used under fair use policy with proper attribution.

Global Excellence & Leadership Awards – Africa 2026 Set to Honor Continent’s Transformative Leaders
NAIROBI, KENYA — Insights Success Media, in collaboration with Insights Excellence Awards, today announced the inaugural Global Excellence & Leadership Awards – Africa 2026, a historic event that will be honoring the continent’s most inventive leaders and visionaries who are redefining Africa’s future. This event will be held on March 21, 2026, at the Radisson Blu in Nairobi, Kenya. This awards platform is Africa’s most important forum for recognizing extraordinary leadership and revolutionary effect across industries. The event, which combines a summit and an awards ceremony, will bring together the continent’s greatest thinkers, including CEOs, entrepreneurs, innovators, and policymakers, for a day of inspiration, acknowledgment, and conversation. The event will recognize individuals and organizations that have proven remarkable innovation, long-term impact, and visionary leadership in a variety of areas. These leaders are the driving force behind Africa’s economic change, and with their ideas that have blossomed into empires with far-reaching implications across the continent and beyond. Under the patronage of leading business dignitaries from Africa and around the globe, the awards ceremony seeks to create a platform where Africa’s voice makes a massive impact. The recognition extends beyond traditional success metrics to celebrate those who have built lasting significance in their communities and industries. The one-day ceremony includes a strategic summit and an awards ceremony, providing delegates with unparalleled networking opportunities and insights from the continent’s most successful leaders. Participants will have important debates about the future of African business, innovation, and leadership while also recognizing outstanding achievements. This ceremony in Africa seeks to elevate acknowledged leaders to the level of global renown, amplifying their stories to inspire others across the continent and around the world. By highlighting these changemakers, the event emphasizes Africa’s expanding presence in the global corporate environment. Business leaders, entrepreneurs, and organizations interested in participating in or learning more about the Global Excellence & Leadership Awards – Africa 2026 should visit the official website at insightsexcellenceawards.com or contact the organizing team directly. About Insights Success Insights Success Media is an international B2B publishing platform operating across 45 countries that showcases visionary leadership and industry transformation. Through digital publications, executive forums, and awards programs, the company connects with business leaders and highlights their transformative achievements. With over 500,000+ professional readers and 1.5 million subscribers worldwide, the organization has established itself as a trusted voice in celebrating excellence across industries. Event Details: Date: March 21, 2026 Venue: Radisson Blu, Nairobi, Kenya Organized by: Insights Success Powered by: Insights Excellence Awards Media Contact: Niwrutti Sawant Email: niwrutti.sawant@insightssuccess.com Phone: +971 55 908 2464 / +1 302 205 1311 Website: insightsexcellenceawards.com
Digital Beachhead Quarterly Magazine, 2025
Digital Beachhead Quarterly Magazine, 2025 Designed to inform, inspire, and spark meaningful dialogue, the publication engages digital leaders, policymakers, defense professionals, and technology innovators. It acts as a central platform for stakeholders navigating the complex and rapidly evolving landscape of digital conflict, innovation, and strategic transformation. Digital Link Quick highlights Quick reads
Cyber Awareness Is Everyone’s Business: A CEO’s Call to Action
By Mike Crandall, CEO In today’s digital-first economy, cybersecurity is no longer just an IT concern, it’s a strategic business priority. As CEO, I’ve seen firsthand how the strength of our organization’s cyber defenses depends not only on our technology stack but on the awareness and behavior of our people. The Human Firewall: Our Greatest Vulnerability and Strength Technology can only do so much. The real risk often lies in human behavior. According to the 2025 “Oh Behave!” Cybersecurity Attitudes and Behaviors Report, 82% of data breaches involve a human element-whether it’s falling for phishing scams, using weak passwords, or failing to update software. Despite growing threats, troubling gaps remain: 41% of employees never use a password manager. Only 41% regularly use multi-factor authentication, even though 77% recognize its importance. 58% of users report receiving no training on AI related security or privacy risks. These numbers are more than statistics, they’re a wake-up call. Leadership Must Set the Tone Cyber awareness starts at the top. When executives prioritize cybersecurity, it sends a clear message: this matters. We’ve made it a point to integrate cyber hygiene into our leadership practices, regular training, phishing simulations, and open conversations about risk. The SANS 2025 Security Awareness Report emphasizes that it takes 3–5 years to influence behavior and 5–10 years to shape culture. That’s why we’re investing now not just in tools, but in people. Training That Drives Results Structured awareness programs don’t just reduce risk-they drive performance. Organizations with formal training programs see 218% higher income per employee compared to those without. And cyber awareness training has been shown to reduce security-related risks by 70%. Yet, 44% of individuals surveyed in 2025 experienced cybercrime that led to data or monetary loss, with younger generations hit hardest. This underscores the need for continuous, adaptive training that evolves with the threat landscape. Building a Culture of Vigilance Cybersecurity is no longer just technical—it’s behavioral. We’re fostering a culture where employees feel empowered to report suspicious activity, ask questions, and take ownership of their digital actions. We’ve also embraced innovative strategies: Just-in-time security nudges that warn users before risky actions. Behavioral analytics to detect anomalies like after hours data transfers. Gamified training and “phish-a-thons” to make learning engaging and memorable. The Bottom Line Cyber awareness is a shared responsibility. As CEO, I’m committed to ensuring our organization doesn’t just react to threats-we anticipate them. We invest in technology, yes, but more importantly, we invest in our people. Let’s make cyber awareness part of our DNA. Because protecting our data means protecting our future. Would you like this formatted into a downloadable PDF or adapted for a specific publication or audience (e.g., internal newsletter, industry journal) Read Also : A Global Leadership Sherpa – Dr. Emmanuel V. Dalavai: Developing Today’s Leaders and Mentoring the Aspiring Leaders of Tomorrow
Secure Compliance Through User Training – Ralf Schwoerer| CEO Silverback Consulting
Introduction As cyber threats grow more sophisticated, compliance has become more than a checklist—it’s a critical part of any organization’s strategy. At Silverback Consulting, we recognize the growing pressure organizations face to meet complex regulatory standards like HIPAA, CMMC, NIST, PCI, and FTC. It’s not enough to rely on technical defenses alone. Every user in your organization must also be prepared to act as a line of defense. Mistakes made by untrained employees can easily lead to compliance failures. That’s why user training is essential. It builds awareness, reduces risk, and strengthens your compliance posture from within. Why User Training Is the Bedrock of Compliance Too often, organizations invest in high-end security infrastructure but overlook the weakest link—human error. Whether it’s falling for a cleverly disguised phishing email or mishandling sensitive data, employees can unintentionally compromise compliance. Our approach at Silverback focuses on proactive user training to create a culture of security awareness that aligns with compliance mandates. Compliance frameworks like CMMC, HIPAA, and NIST 800-171 mandate regular training to ensure that personnel understand their security responsibilities. Effective training ensures that users are not only aware of risks but also equipped to respond to them appropriately. It’s not just about ticking boxes—it’s about enabling behavioral change that enhances security posture. Integrating Phishing Simulations Into Compliance Strategy A key component of our compliance training programs is the inclusion of phishing simulation exercises. These realistic scenarios test and reinforce user awareness without exposing your network to actual threats. By conducting periodic phishing tests, we help organizations: Identify users most at risk Provide targeted remediation training Reduce overall susceptibility to social engineering attacks Simulations are tailored to mimic current attack vectors and reinforce lessons learned in formal training sessions. These exercises satisfy various compliance requirements, including FTC Safeguards Rule mandates, by demonstrating due diligence in employee security education. Tailored Compliance Training for Your Industry Needs At Silverback Consulting, we customize our training modules based on the specific regulatory requirements your business must adhere to: HIPAA Compliance Training: Focused on protecting electronic protected health information (ePHI), including secure data handling and breach notification protocols. CMMC Certification Training: For DoD contractors, we provide level-specific training aligned with the latest Cybersecurity Maturity Model Certification guidelines. PCI DSS Training: Ensures personnel who handle cardholder data are trained to follow Payment Card Industry Data Security Standard practices. NIST-Based Security Awareness: Aligns with NIST SP 800-53 and NIST 800-171, promoting a culture of responsibility in managing controlled unclassified information (CUI). By aligning user training with these standards, we help reduce the likelihood of audit findings and penalties, while enhancing your organization’s overall security maturity. Continuous Learning: The Key to Long-Term Compliance Compliance is not a one-and-done project. It is an ongoing commitment that demands regular updates, refreshers, and adaptations to emerging threats. That’s why our programs are designed with a continuous training cycle, including: Regularly updated course content Microlearning modules for retention Monthly phishing simulations Reporting dashboards for compliance tracking Our learning management systems provide administrators and compliancy officers with full visibility into employee progress, helping you document compliance efforts and present audit-ready reports at any time. Linking Compliance With Organizational Risk Reduction Organizations that embed user training into their compliance efforts see measurable improvements in risk mitigation. Employees become more vigilant about: Recognizing and reporting phishing emails Following secure data transfer protocols Understanding acceptable use policies Practicing physical and digital asset protection This risk reduction directly supports FTC and HIPAA breach prevention requirements, while fulfilling PCI and CMMC expectations for staff security awareness. We don’t just teach what compliance is—we build operational habits that sustain it. Metrics-Driven Compliance Training Outcomes Our philosophy at Silverback Consulting is that what gets measured gets managed. That’s why we integrate actionable metrics into every aspect of our training programs, including: Phishing susceptibility rates over time Training completion rates and score improvements Policy acknowledgment tracking Behavioral trends among different departments These insights allow compliance officers, IT directors, and HR teams to fine-tune the training process, allocate resources effectively, and prepare detailed compliance documentation. Bridging the Gap Between Policy and Practice Many organizations have documented compliance policies, but without effective training, those policies are not actionable. Our training bridges this gap by translating policy language into real-world scenarios that employees can understand and apply. For example, understanding what constitutes a HIPAA violation becomes much more intuitive when employees are shown simulated cases where mishandling data led to real-world consequences. Likewise, understanding CMMC controls becomes easier when training walks users through examples relevant to their actual job roles.
Let Me Explain To You Why I Say No Every Time You Ask to Make Your Password Shorter: The Downfall of a 158-Year-Old Company Due to Just One Weak Password
If there is one universal truth out there today in modern offices, it’s this: everyone hates password requirements. I can’t count how many times a coworker has complained to me personally about how hard to remember their password is because they had to use random words and numbers instead of their child’s name and birthdate. But I get it, the password fatigue is real. Between work accounts, streaming services, banking apps, and the three different logins required just to order a coffee, it’s no wonder everyone defaults to some version of “123456.” They sigh, roll their eyes, and think: What’s the worst that could happen?’ Turns out, quite a lot. This year, just a few short months ago, a 158-year-old logistics company (one that has survived two worlds, multiple recessions, and the invention of the car) was forced to close its doors because of one employee’s weak password. That’s it. No Criminal Minds-type hacking scene, no spy movie break in. Just guessed login credentials. That, combined with no MFA, disaster recovery processes, or zero trust architecture, led to the eventual downfall that put 700 people out of work. This is the story of KNP Logistics Group. Let me start by setting the day. It’s a cloudy Tuesday morning in June 2025, at the KNP Logistics yard in the UK. KNP, founded in 1865 as Knights of Old using horse drawn wagons (yeah, they’re that old), were now running a fleet of around 500 lories. If you asked KNP, they’ll say its IT complied with industry standards and it had taken out insurance against cyber-attacks. You know, the bare minimum. Around midday employees stated that they noticed the phones stopped ringing. By that evening, the company’s internal systems had completely shut down. Invoices disappeared, trucks couldn’t be routed, and the dispatch software showed nothing but error messages. So what happened? A gang of hackers, known as Akira, got in to KNP’s system by simply guessing an employee’s password. And because Multifactor Authentication (MFA) was not required or in place, the guessed password turned in to the best skeleton key any criminal could ask for. Akira was able to stroll right through the front door (digitally, of course) and do what they do best: explore, spread, and seize control. Think of it like burglars who not only rob your house but also change the locks, shred your family photos, and take the spare keys to the garage. Within just days, critical systems were encrypted and everything was deleted, including the supposedly safe backups. Later that same month KNP received a ransom note demanding money in return for KNP’s data. “If you’re reading this it means the internal infrastructure of your company is fully or partially dead…. Let’s keep all the tears and resentment to ourselves and try to build a constructive dialogue,” the ransom note read. The hackers didn’t ask for a specific sum of money in the note itself, but a specialist ransomware negotiation firm estimates it could be as much as £5 million. In July, KNP halts most of its operations as employees are unable to access payroll or dispatch systems. As stated earlier, it is true that KNP had cyber insurance. But that doesn’t mean it was great insurance. Take for example having car insurance but realizing too late that it doesn’t cover Godzilla attacks. That’s what happened with KNP. No amount of fine print in the world is going to help when your car has been stomped to a pancake. KNP Leadership slowly began to realize that restoration was impossible, and by September the company entered administration, ceasing all operations after 158 years. The human cost behind this incident was devasting. Drivers, warehouse staff, office managers — people who had built careers with the company — were left wondering how a simple password mistake could erase their livelihoods overnight. One dispatcher was quoted as describing it as “watching a giant slowly tip over.” First the screens froze, then the trucks stopped, and then, just like that, the entire company was gone. For KNP’s customers and suppliers, the closing caused ripple effects across the logistics chain in the UK. Contracts were voided, deliveries were left stranded, and relationships that had lasted over a hundred years were severed. If the whole thing wasn’t so devastating it would almost be funny. A company that survived two world wars and the Great Depression was brought down by what? A password so weak a hacker could stumble across it in an afternoon. Cyber Security experts have long stated that the most common passwords (i.e. Password123, Welcome2025, 123456) are basically invitations to criminals. And the irony here is that KNP wasn’t reckless with their security. They did what most mid-sized logistics firms do to meet industry standards; they ran antivirus software, kept up with compliance, and carried cyber insurance. But attackers aren’t measuring you against the industry standard, they’re measuring you against the weakest point in your defenses. And in KNP’s case, that point was wide open. This lesson isn’t a new one, but KNP’s downfall puts it back in bright, shining lights: in 2025, one bad password can still kill a company. If a company with more than a century of experience could vanish almost overnight, who’s safe? The reality is no one. Every modern business has a digital aspect to it. Healthcare, education, finance, manufacturing – all industries where downtime can be catastrophic – face the exact same threat. Attackers don’t need high end devices or spy equipment to break in to a business when human laziness does all the work for them. So what can you do when every business is only as strong as its weakest password? A lot actually: Use stronger passwords: Yes, it’s annoying. No, your child’s name plus a number isn’t enough. Enable MFA everywhere: If you hate typing in a code, imagine how much you’ll hate explaining to 700 employees that they’re out of work because you skipped it. Backups need to be untouchable: If